AppleがiPhoneやiPadなど向けiOS 26.7.3とiPadOS 26.7.3をリリース!
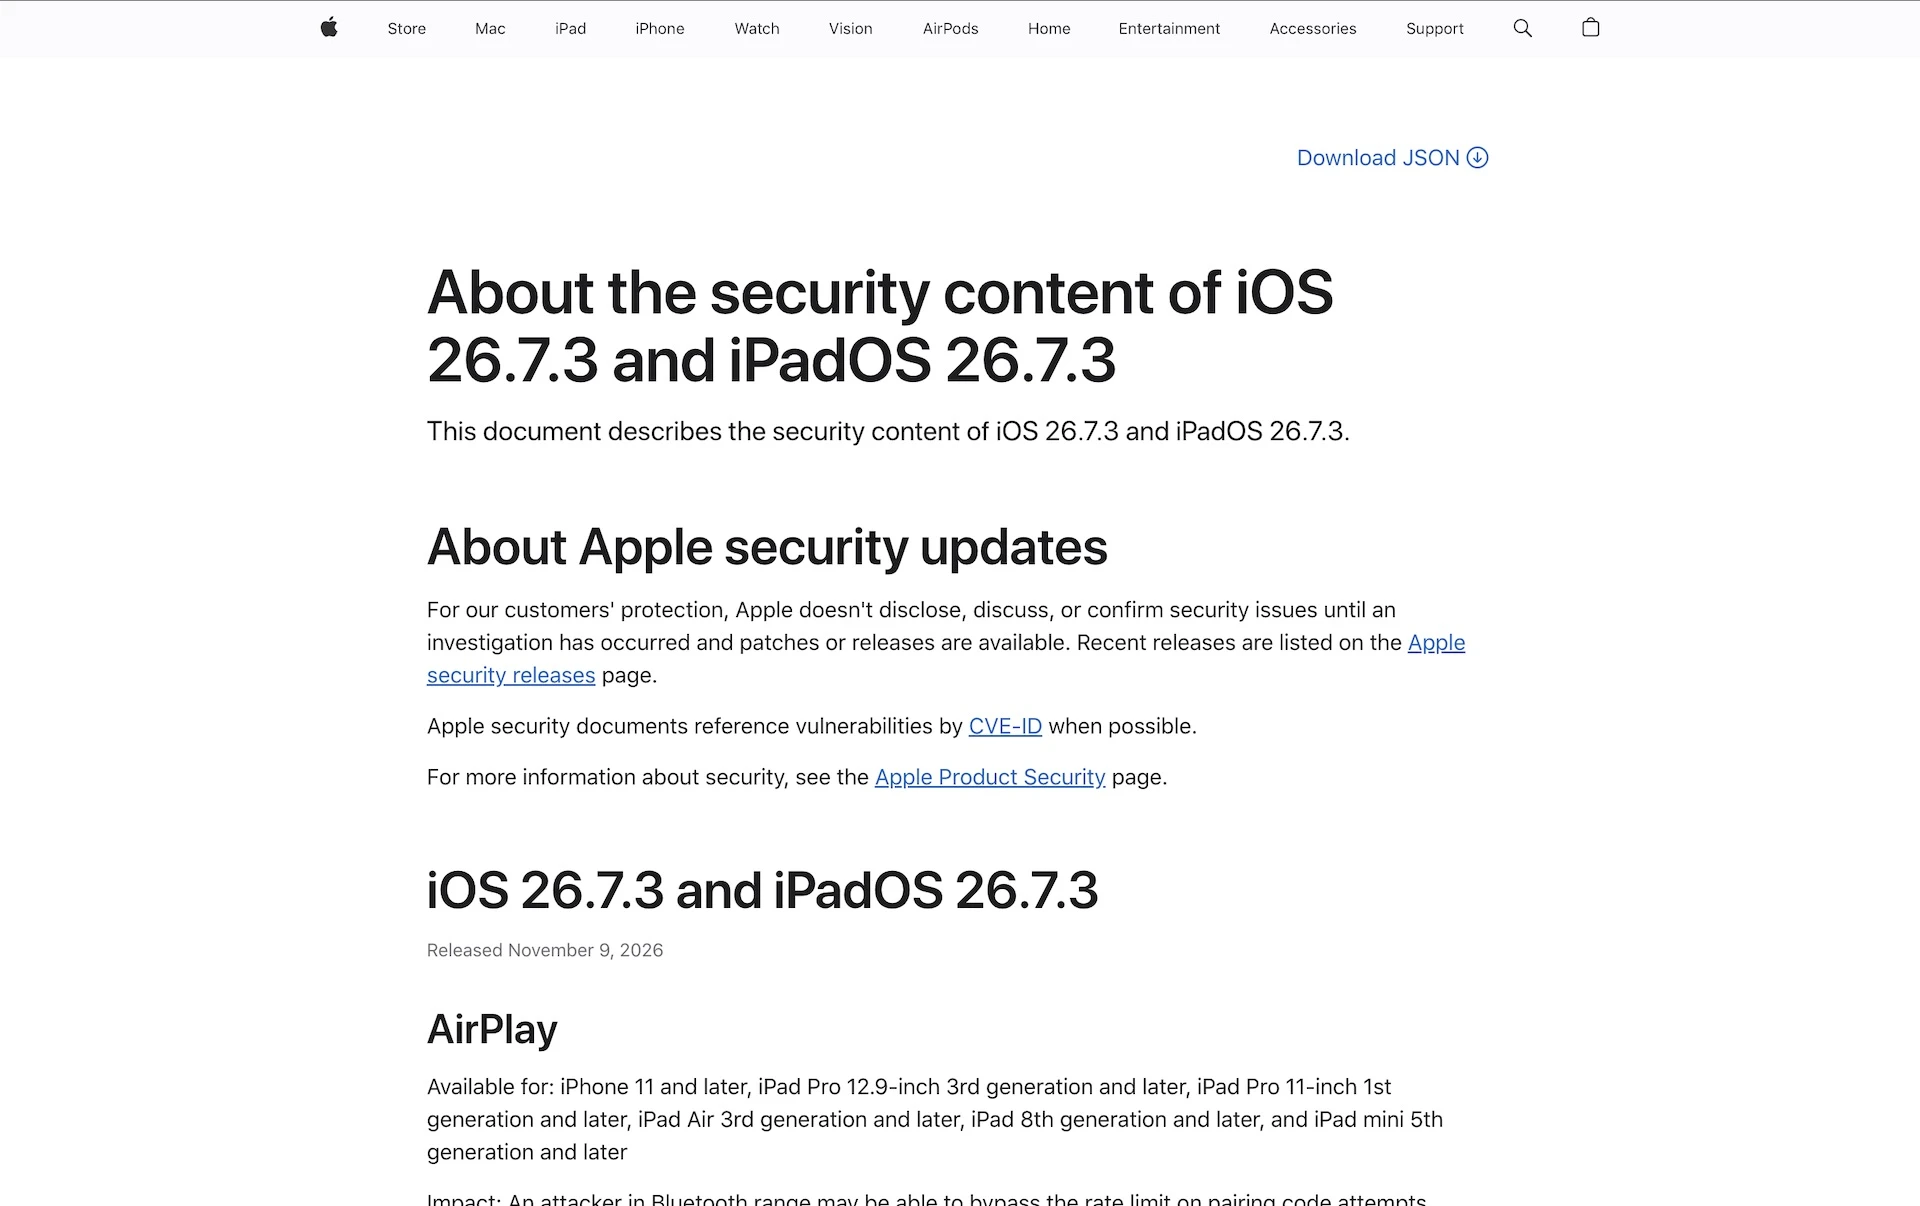
Appleは9日(現地時間)、同社が販売するスマートフォン(スマホ)「iPhone」シリーズ向けプラットフォーム「iOS」とタブレット「iPad」シリーズ向けプラットフォーム「iPadOS」の最新バージョン「iOS 26.7.3(23H131)」および「iPadOS 26.7.3(23H131)」を提供開始したとお知らせしています。変更点はセキュリティー修正だとのことで、CVEに登録されている脆弱性としてはMessages関連の「CVE-2026-113961」や「CVE-2026-113960」などの8個の脆弱性が修正されているということです。
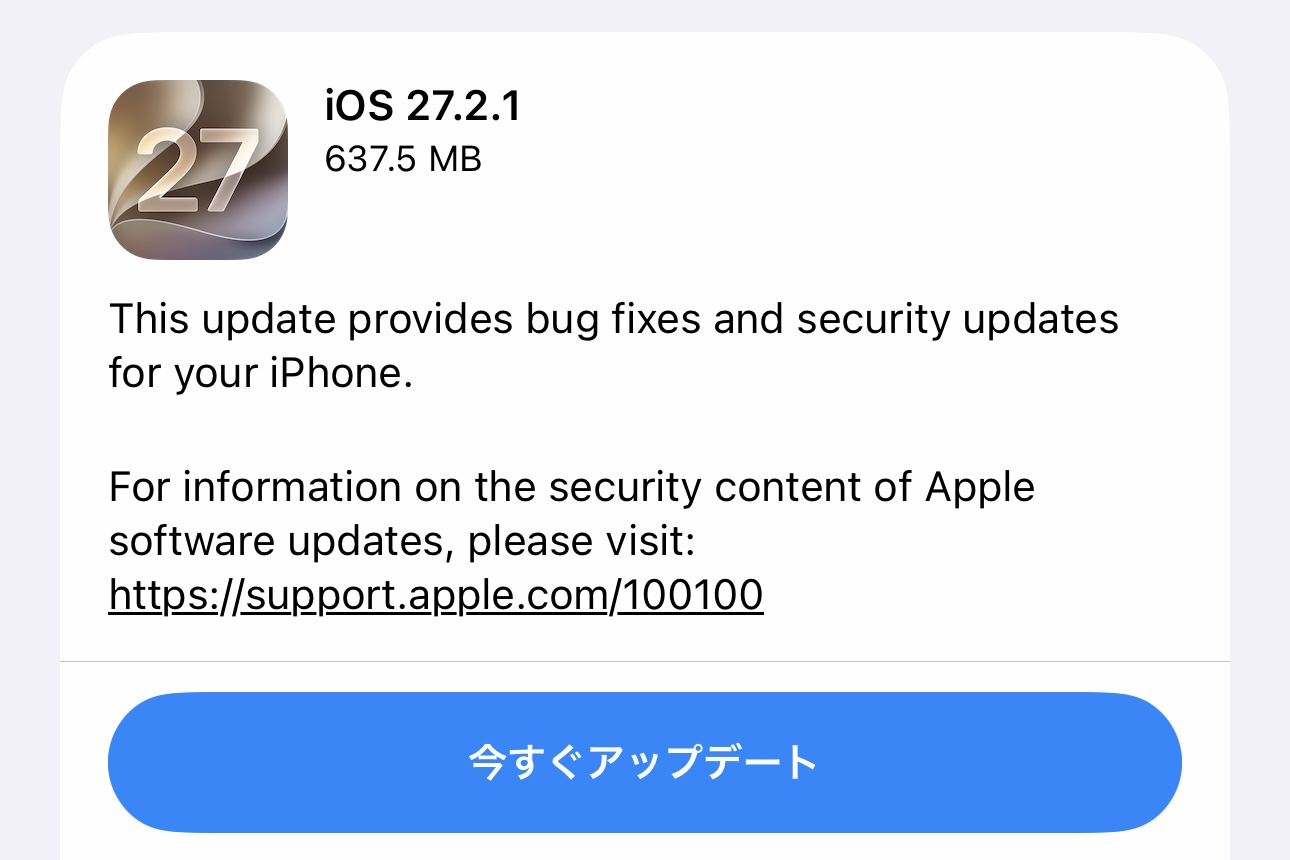
対象はiOS 26およびiPadOS 26の対応機種で、iOS 26ではiPhone 11シリーズ以降やiPhone SE(第2世代)以降が対象、iPadOS 26ではiPad(第8世代)以降やiPad mini(第5世代)以降、iPad Air(第3世代)以降、12.9インチiPad Pro(第3世代)以降および11インチiPad Pro(第1世代)以降のiPad Proシリーズが対象となり、各製品にて無料で更新可能です。なお、すでに紹介しているように次の最新バージョン「iOS 27」や「iPadOS 27」も提供開始されているため、iOS 27やiPadOS 27の対象機種はiOS 27.2.1やiPadOS 27.2.1またはiOS 26.7.3やiPadOS 26.7.3を選んで更新します。
iPhone向けのiOSやiPad向けのiPadOSの最新メジャーバージョンとして先ごろよりiOS 26.0とiPadOS 26.0が提供開始されていましたが、これらに続けて新機能が追加されたiOS 26.1とiPadOS 26.1、iOS 26.2とiPadOS 26.2、iOS 26.3とiPadOS 26.3、iOS 26.4とiPadOS 26.4、iOS 26.5とiPadOS 26.5、iOS 26.6とiPadOS 26.6、iOS 26.7とiPadOS 26.7が提供され、その後、iOS 26.7とiPadOS 26.7の不具合や脆弱性を修正したiOS 26.7.1〜26.7.2やiPadOS 26.7.1〜26.7.2がリリースされてきましたが、今回、複数の脆弱性の修正が行われたiOS 26.7.3およびiPadOS 26.7.3がリリースされました。iOS 26.7.3およびiPadOS 26.7.3の対象機種は以下の通り。
<iOS 26対応製品>
・iPhone 17e
・iPhone 17
・iPhone 17 Pro
・iPhone 17 Pro Max
・iPhone Air
・iPhone 16e
・iPhone 16
・iPhone 16 Plus
・iPhone 16 Pro
・iPhone 16 Pro Max
・iPhone 15
・iPhone 15 Plus
・iPhone 15 Pro
・iPhone 15 Pro Max
・iPhone 14
・iPhone 14 Plus
・iPhone 14 Pro
・iPhone 14 Pro Max
・iPhone 13
・iPhone 13 mini
・iPhone 13 Pro
・iPhone 13 Pro Max
・iPhone 12
・iPhone 12 mini
・iPhone 12 Pro
・iPhone 12 Pro Max
・iPhone 11
・iPhone 11 Pro
・iPhone 11 Pro Max
・iPhone SE(第3世代)
・iPhone SE(第2世代)
<iPadOS 26対応製品>
・iPad(第8世代)
・iPad(第9世代)
・iPad(第10世代)
・iPad(A16)
・iPad mini(第5世代)
・iPad mini(第6世代)
・iPad mini(A17 Pro)
・iPad Air(第3世代)
・iPad Air(第4世代)
・iPad Air(第5世代)
・11インチiPad Air(M2)
・11インチiPad Air(M3)
・11インチiPad Air(M4)
・13インチiPad Air(M2)
・13インチiPad Air(M3)
・13インチiPad Air(M4)
・11インチiPad Pro(第1世代)
・11インチiPad Pro(第2世代)
・11インチiPad Pro(第3世代)
・11インチiPad Pro(第4世代)
・11インチiPad Pro(M4)
・11インチiPad Pro(M5)
・12.9インチiPad Pro(第3世代)
・12.9インチiPad Pro(第4世代)
・12.9インチiPad Pro(第5世代)
・12.9インチiPad Pro(第6世代)
・13インチiPad Pro(M4)
・13インチiPad Pro(M5)
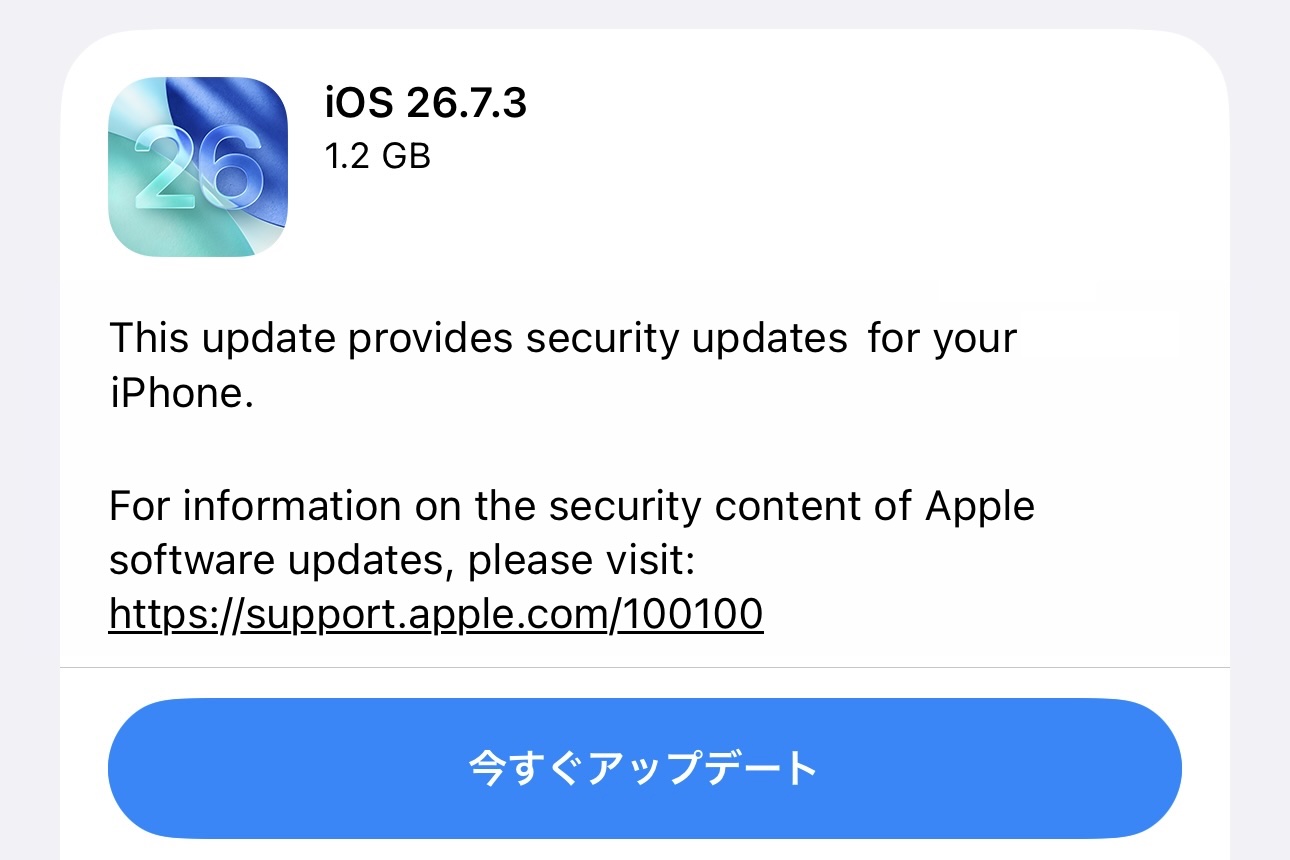
更新は従来通り各製品本体のみでOTA(On-The-Air)によりダウンロードで行え、方法としては、「設定」→「一般」→「ソフトウェア・アップデート」から行え、単体でアップデートする場合のダウンロードサイズは手持ちのiPhone 13 Pro MaxでiOS 26.7.2からだと1.2GBとなっています。またiTunesをインストールしたWindowsおよびMacとUSB-Lightningケーブルで接続しても実施できます。なお、Appleが案内しているアップデートの内容およびセキュリティーコンテンツの修正は以下の通り。
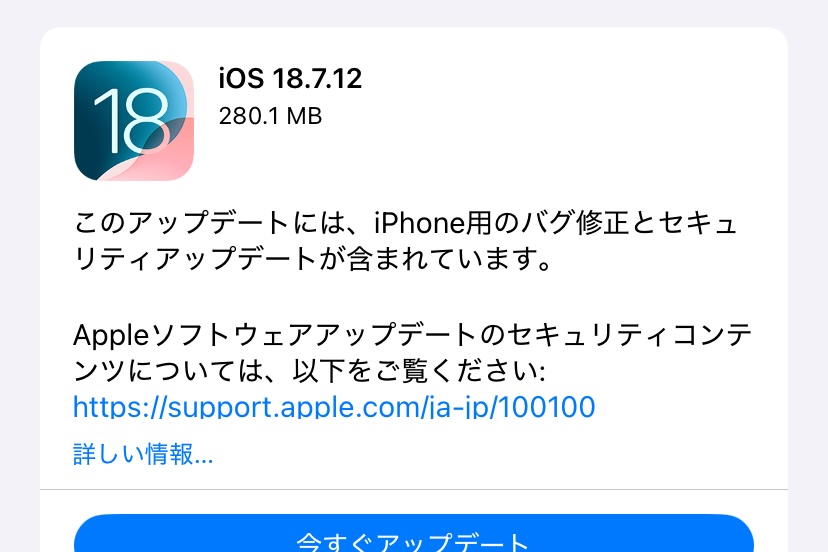
iOS 26.7.3
このアップデートには、iPhone用のセキュリティ修正が含まれています。Appleソフトウェアアップデートのセキュリティコンテンツについては、以下をご覧ください: https://support.apple.com/100100
iPadOS 26.7.3
このアップデートには、iPad用のセキュリティ修正が含まれています。Appleソフトウェアアップデートのセキュリティコンテンツについては、以下をご覧ください: https://support.apple.com/100100
iOS 26.7.3 and iPadOS 26.7.3
Released November 9, 2026– AirPlay
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: An attacker in Bluetooth range may be able to bypass the rate limit on pairing code attempts
Description: A logic issue was addressed with improved state management.
CVE-2026-113968: Apple– Bluetooth
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: An attacker in Bluetooth range may be able to corrupt process memory
Description: A use-after-free issue was addressed with improved memory management.
CVE-2026-113970: Apple– brotli
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: Processing maliciously crafted input may lead to memory corruption
Description: An out-of-bounds write issue was addressed with improved input validation.
CVE-2026-111497– CoreUtils
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: A malicious Bluetooth device may be able to establish a pairing without user interaction
Description: This issue was addressed with improved checks.
CVE-2026-113965: Apple– CoreUtils
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: An attacker in Bluetooth range may be able to bypass the rate limit on pairing code attempts and pair with a device without user interaction
Description: A logic issue was addressed with improved state management.
CVE-2026-113964: an anonymous researcher– Messages
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: A user added to an iMessage group may be able to access messages sent before they joined
Description: This issue was addressed by removing the vulnerable code.
CVE-2026-113960: an anonymous researcher– Messages
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: A remote attacker may be able to join an iMessage group chat and receive its messages
Description: An authorization issue was addressed with improved validation.
CVE-2026-113961: an anonymous researcher– rapportd
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: An attacker on the same network may be able to bypass the rate limit on AirPlay pairing code attempts
Description: A logic issue was addressed with improved state management.
CVE-2026-113969: Apple

■関連リンク
・エスマックス(S-MAX)
・エスマックス(S-MAX) smaxjp on Twitter
・S-MAX – Facebookページ
・iOS 26 関連記事一覧 – S-MAX
・iPadOS 26 関連記事一覧 – S-MAX
・iOS 26 のアップデートについて – Apple サポート (日本)
・iPadOS 26 のアップデートについて – Apple サポート (日本)
・iOS 26.7.3およびiPadOS 26.7.3のセキュリティコンテンツについて – Apple サポート (日本)
・Apple セキュリティアップデート – Apple サポート
コメント