AppleがiPhoneやiPadなど向けiOS 26.7とiPadOS 26.7をリリース!
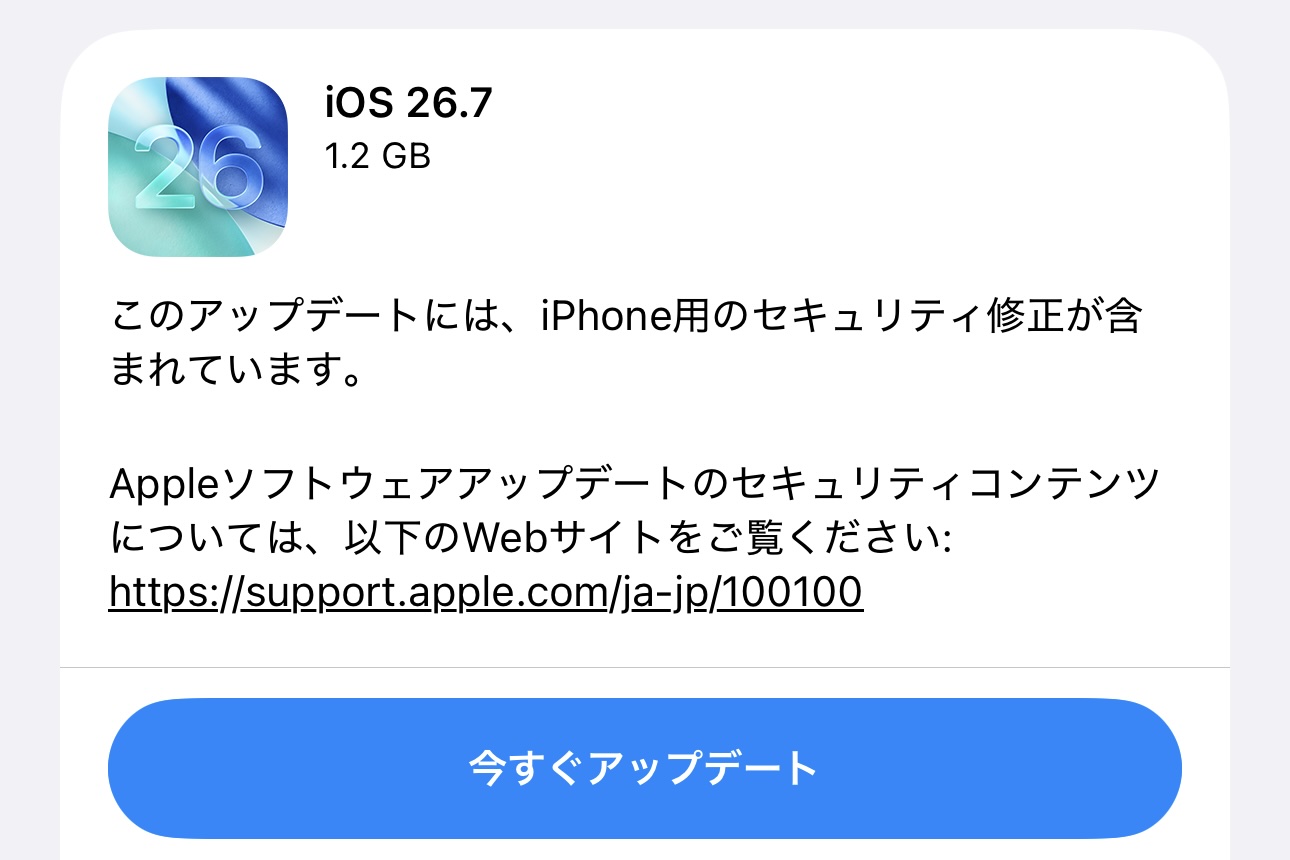
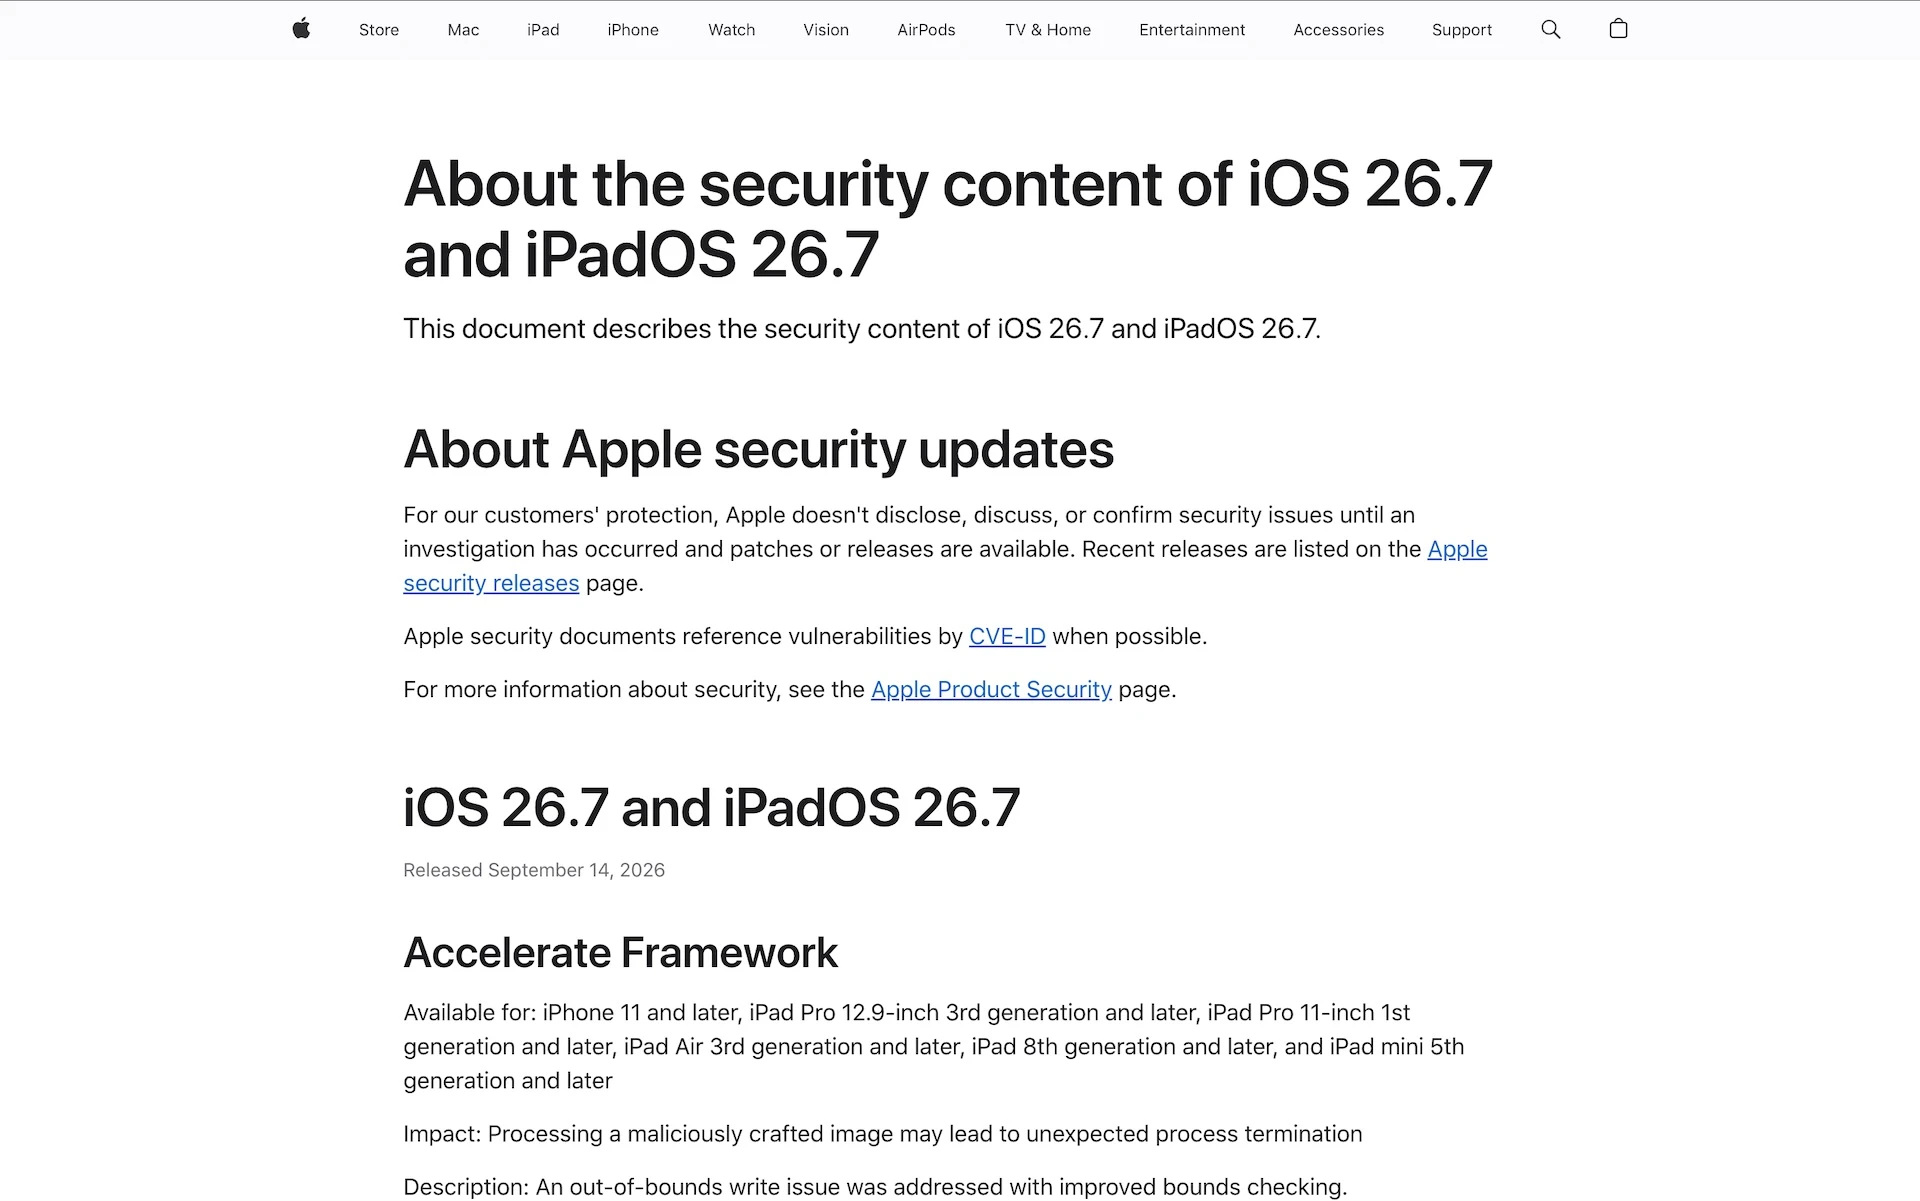
Appleは14日(現地時間)、同社が販売するスマートフォン(スマホ)「iPhone」シリーズ向けプラットフォーム「iOS」とタブレット「iPad」シリーズ向けプラットフォーム「iPadOS」の最新バージョン「iOS 26.7(23H24)」および「iPadOS 26.7(23H24)」を提供開始したとお知らせしています。変更点はセキュリティー修正だとのことで、CVEに登録されている脆弱性としてはKernelに関する「CVE-2026-28968」および「CVE-2026-43689」、「CVE-2026-65377」などの82個の脆弱性が修正されており、同社ではいくつかの脆弱性が悪用された可能性があるという報告を認識していると説明しています。
対象はiOS 26およびiPadOS 26の対応機種で、iOS 26ではiPhone 11シリーズ以降やiPhone SE(第2世代)以降が対象、iPadOS 26ではiPad(第8世代)以降やiPad mini(第5世代)以降、iPad Air(第3世代)以降、12.9インチiPad Pro(第3世代)以降および11インチiPad Pro(第1世代)以降のiPad Proシリーズが対象となり、各製品にて無料で更新可能です。なお、すでに紹介しているように次の最新バージョン「iOS 27」や「iPadOS 27」も提供開始されているため、iOS 27やiPadOS 27の対象機種はiOS 27.0やiPadOS 27.0またはiOS 26.7やiPadOS 26.7を選んで更新します。
iPhone向けのiOSやiPad向けのiPadOSの最新メジャーバージョンとして先ごろよりiOS 26.0とiPadOS 26.0が提供開始されていましたが、これらに続けて新機能が追加されたiOS 26.1とiPadOS 26.1、iOS 26.2とiPadOS 26.2、iOS 26.3とiPadOS 26.3、iOS 26.4とiPadOS 26.4、iOS 26.5とiPadOS 26.5、iOS 26.6とiPadOS 26.6が提供され、その後、iOS 26.6とiPadOS 26.6の不具合や脆弱性を修正したiOS 26.6.1〜26.6.2やiPadOS 26.6.1〜26.6.2がリリースされてきましたが、今回、複数の脆弱性の修正が行われたiOS 26.7およびiPadOS 26.7がリリースされました。iOS 26.7およびiPadOS 26.7の対象機種は以下の通り。
<iOS 26対応製品>
・iPhone 17e
・iPhone 17
・iPhone 17 Pro
・iPhone 17 Pro Max
・iPhone Air
・iPhone 16e
・iPhone 16
・iPhone 16 Plus
・iPhone 16 Pro
・iPhone 16 Pro Max
・iPhone 15
・iPhone 15 Plus
・iPhone 15 Pro
・iPhone 15 Pro Max
・iPhone 14
・iPhone 14 Plus
・iPhone 14 Pro
・iPhone 14 Pro Max
・iPhone 13
・iPhone 13 mini
・iPhone 13 Pro
・iPhone 13 Pro Max
・iPhone 12
・iPhone 12 mini
・iPhone 12 Pro
・iPhone 12 Pro Max
・iPhone 11
・iPhone 11 Pro
・iPhone 11 Pro Max
・iPhone SE(第3世代)
・iPhone SE(第2世代)
<iPadOS 26対応製品>
・iPad(第8世代)
・iPad(第9世代)
・iPad(第10世代)
・iPad(A16)
・iPad mini(第5世代)
・iPad mini(第6世代)
・iPad mini(A17 Pro)
・iPad Air(第3世代)
・iPad Air(第4世代)
・iPad Air(第5世代)
・11インチiPad Air(M2)
・11インチiPad Air(M3)
・11インチiPad Air(M4)
・13インチiPad Air(M2)
・13インチiPad Air(M3)
・13インチiPad Air(M4)
・11インチiPad Pro(第1世代)
・11インチiPad Pro(第2世代)
・11インチiPad Pro(第3世代)
・11インチiPad Pro(第4世代)
・11インチiPad Pro(M4)
・11インチiPad Pro(M5)
・12.9インチiPad Pro(第3世代)
・12.9インチiPad Pro(第4世代)
・12.9インチiPad Pro(第5世代)
・12.9インチiPad Pro(第6世代)
・13インチiPad Pro(M4)
・13インチiPad Pro(M5)
更新は従来通り各製品本体のみでOTA(On-The-Air)によりダウンロードで行え、方法としては、「設定」→「一般」→「ソフトウェア・アップデート」から行え、単体でアップデートする場合のダウンロードサイズは手持ちのiPhone 15 Pro MaxでiOS 26.6.2からだと1.2GBとなっています。またiTunesをインストールしたWindowsおよびMacとUSB-Lightningケーブルで接続しても実施できます。なお、Appleが案内しているアップデートの内容およびセキュリティーコンテンツの修正は以下の通り。
iOS 26.7
このアップデートには、iPhone用のセキュリティ修正が含まれています。Appleソフトウェアアップデートのセキュリティコンテンツについては、以下のWebサイトをご覧ください: https://support.apple.com/ja-jp/100100
iPadOS 26.7
このアップデートには、iPad用のセキュリティ修正が含まれています。Appleソフトウェアアップデートのセキュリティコンテンツについては、以下のWebサイトをご覧ください: https://support.apple.com/ja-jp/100100
iOS 26.7 and iPadOS 26.7
Released September 14, 2026– Accelerate Framework
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: Processing a maliciously crafted image may lead to unexpected process termination
Description: An out-of-bounds write issue was addressed with improved bounds checking.
CVE-2026-86882: Peter Malone– Accessibility
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: An app may be able to access sensitive user data
Description: This issue was addressed with improved data protection.
CVE-2026-43664: Stuart Wallace, Rosyna Keller of Totally Not Malicious Software, Jian Lee (@speedyfriend433), Ilya Andr (andrd3v), Gongyu Ma (@Mezone0), David Strnadel, Daniel Febrero, CJ Vana, Asaf Cohen– APFS
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: An app may be able to cause unexpected system termination or write kernel memory
Description: An out-of-bounds write issue was addressed with improved bounds checking.
CVE-2026-84523: Cem Onat Karagun, an anonymous researcher– Apple Neural Engine
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: An app may be able to cause unexpected system termination
Description: An integer overflow was addressed with improved input validation.
CVE-2026-65408: tamdao– AppleAVD
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: An app may be able to cause unexpected system termination
Description: A use after free issue was addressed with improved memory management.
CVE-2026-65407: Franco Belman at Blackwing Intelligence– AppleDouble
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: Mounting a disk image with maliciously crafted files may lead to unexpected system termination
Description: An out-of-bounds write issue was addressed with improved bounds checking.
CVE-2026-84519: Richard Zana– AuthKit
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: A local app may be able to read a persistent account identifier
Description: A permissions issue was addressed with additional restrictions.
CVE-2026-84583: Zhongcheng Li from IES Red Team– AVEVideoEncoder
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: An app may be able to cause unexpected system termination
Description: The issue was addressed with improved checks.
CVE-2026-65410: Calif.io in collaboration with Claude and Anthropic Research– AVEVideoEncoder
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: An app may be able to cause unexpected system termination
Description: A type confusion issue was addressed with improved memory handling.
CVE-2026-84616: Peter Malone– AVEVideoEncoder
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: A sandboxed app may be able to execute arbitrary code with kernel privileges
Description: A race condition was addressed with improved state management.
CVE-2026-84607: Ruslan Dautov– BackgroundAssets
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: An app may be able to access sensitive user data
Description: A logic issue was addressed with improved validation.
CVE-2026-65406: Ye Zhang (@VAR10CK) of Baidu Security– Bluetooth
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: A remote attacker may be able to cause unexpected app termination or arbitrary code execution
Description: An out-of-bounds write issue was addressed with improved bounds checking.
CVE-2026-65414– copyfile
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: An archive may be able to bypass Gatekeeper
Description: A file quarantine bypass was addressed with additional checks.
CVE-2026-65399: Rishabh Jain (rjcyber) of cyberplanet, Pasquale Scola, an anonymous researcher– CoreMedia
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: Processing a maliciously crafted video file may lead to unexpected app termination
Description: An out-of-bounds write issue was addressed with improved bounds checking.
CVE-2026-65344: Siyeong kim– CoreMedia
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: A sandboxed process may be able to circumvent sandbox restrictions
Description: An out-of-bounds write issue was addressed with improved bounds checking.
CVE-2026-86876: Chris Bailey – Short Circuit– CoreMedia Video Toolbox
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: Processing a maliciously crafted video file may lead to unexpected app termination or corrupt process memory
Description: The issue was addressed with improved memory handling.
CVE-2026-43702: Nathaniel Oh (@calysteon)– CoreML
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: A sandboxed app may be able to access restricted files
Description: A permissions issue was addressed with improved path validation.
CVE-2026-84624: AL Najafi, tamdao– CoreMotion
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: An app may be able to access motion data from headphones without user consent
Description: An authorization issue was addressed with improved validation.
CVE-2026-43737: Stuart Wallace– CoreText
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: Processing web content may lead to a denial-of-service
Description: A null pointer dereference was addressed with improved input validation.
CVE-2026-65412: Pavan Nallamothu– DeviceCheck
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: An app may be able to read persistent device identifiers
Description: An authorization issue was addressed with improved access control.
CVE-2026-84612: N.M.Praveen Nawarathne (@zblockrat), James Gill (@jjtech@infosec.exchange)– Disk Images
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: An app may be able to cause unexpected system termination
Description: The issue was addressed with improved memory handling.
CVE-2026-84552: Tommy DeVoss from Braze Security Team (@thedawgyg), flower xu, Adriatik Raci, PETOWORKS의 Bugeun Choi (@Bugeun), Peter Malone, Hyunwoo Kim (@v4bel), Daisuke Hatakeyama and Ryohei Ueki (@SYZD Research)– exFAT
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: Mounting a maliciously crafted volume may lead to unexpected system termination
Description: A heap buffer overflow was addressed with improved bounds checking.
CVE-2026-84510: Richard Zana, Meta Red Team X – Nik Tsytsarkin– file_cmds
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: Extracting a maliciously crafted archive may allow an attacker to write arbitrary files
Description: A path handling issue was addressed with improved validation.
CVE-2026-84534: Geoffrey Lovelace– FontParser
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: Processing a maliciously crafted font file may lead to unexpected app termination
Description: An out-of-bounds read was addressed with improved bounds checking.
CVE-2026-84524: an anonymous researcher– Foundation
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: An app may be able to cause a denial of service
Description: A type confusion issue was addressed with improved memory handling.
CVE-2026-65409: Bruce Dang of Calif.io in collaboration with Claude and Anthropic Research– Graphics
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: An app may be able to cause unexpected system termination
Description: A race condition was addressed with improved state handling.
CVE-2026-84492: Tommy DeVoss from Braze Security Team (@thedawgyg), Jiyong Yang– ImageIO
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: Processing a maliciously crafted image may result in disclosure of process memory
Description: An uninitialized memory issue was addressed with improved memory initialization.
CVE-2026-84564: Justin O’Leary– ImageIO
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: Processing a maliciously crafted file may lead to unexpected app termination
Description: The issue was addressed with improved bounds checks.
CVE-2026-64758: 진규정 (Gyujeong Jin, @G1uN4sh)– ImageIO
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: Processing a maliciously crafted image may corrupt process memory
Description: A buffer overflow issue was addressed with improved memory handling.
CVE-2026-43661: Gandalf4a of PKU-ICODE, Anton Pakhunov, an anonymous researcher– ImageIO
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: Processing a maliciously crafted image may lead to unexpected app termination
Description: An out-of-bounds write issue was addressed with improved bounds checking.
CVE-2026-86869: Niels Hofmans, Meta Red Team X, Geonha Lee (@leegn4a), Chris Bailey – Short Circuit– ImageIO
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: Processing a maliciously crafted image may result in memory corruption
Description: An out-of-bounds write issue was addressed with improved bounds checking.
CVE-2026-65395: Mateusz Jurczyk of Google Project Zero, Varik Matevosyan– IOGPUFamily
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: An app may be able to cause unexpected system termination
Description: A race condition was addressed with improved state handling.
CVE-2026-43743: Lyutoon, Dun– Kernel
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: A local attacker may be able to cause unexpected system termination or corrupt kernel memory
Description: The issue was addressed with improved memory handling.
CVE-2026-84566: Bernhard Jackiewicz– Kernel
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: An app may be able to cause unexpected system termination or corrupt kernel memory
Description: An out-of-bounds write issue was addressed with improved bounds checking.
CVE-2026-28968: Svetoslav Stolarov & Aisa Fox, Josh Maine of Calif.io, genter0, Dun– Kernel
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: A malicious app may be able to gain root privileges
Description: A permissions issue was addressed with additional restrictions.
CVE-2026-43689: Andreas Jaegersberger & Ro Achterberg of Nosebeard Labs– Kernel
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: An app may be able to cause unexpected system termination
Description: A memory corruption issue was addressed with improved memory handling.
CVE-2026-65377: Ye Zhang (@VAR10CK) of Baidu Security, Billy Jheng Bing Jhong and Pan Zhenpeng (@Peterpan0927) of STAR Labs SG Pte. Ltd.– Kernel
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: Connecting to a malicious NFS server may disclose kernel memory
Description: The issue was addressed with improved memory handling.
CVE-2026-43687: R4mbb of KRsecurity, Peter Malone– Kernel
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: An app may be able to cause unexpected system termination or corrupt kernel memory
Description: A use-after-free issue was addressed with improved memory management.
CVE-2026-43684: Peter Malone– Kernel
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: Connecting to a malicious NFS server may lead to kernel memory corruption
Description: A use-after-free issue was addressed with improved memory management.
CVE-2026-43686: Peter Malone– Kernel
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: An app may be able to determine kernel memory layout
Description: A memory initialization issue was addressed with improved memory handling.
CVE-2026-65405: Billy Jheng Bing Jhong and Pan Zhenpeng (@Peterpan0927) of STAR Labs SG Pte. Ltd.– Kernel
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: An app may be able to cause unexpected system termination
Description: A race condition was addressed with improved state handling.
CVE-2026-84630: Tristan Madani (@TristanInSec) from Talence Security
CVE-2026-65360: Billy Jheng Bing Jhong and Pan Zhenpeng (@Peterpan0927) of STAR Labs SG Pte. Ltd.– Kernel
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: An app may be able to disclose kernel memory
Description: An information disclosure issue was addressed with improved memory management.
CVE-2026-84530: Vladislav Shevchenko (Positive Technologies)– Kernel
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: An app with root privileges may be able to read uninitialized kernel memory
Description: A memory initialization issue was addressed with improved memory handling.
CVE-2026-84622: Hiroki Imai (LAC Co., Ltd.)– Kernel
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: An app may be able to cause unexpected system termination
Description: A type confusion issue was addressed with improved checks.
CVE-2026-84602: Billy Jheng Bing Jhong and Pan Zhenpeng (@Peterpan0927) of STAR Labs SG Pte. Ltd.– Kernel
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: An app may be able to cause unexpected system termination
Description: A use after free issue was addressed with improved memory management.
CVE-2026-65402: Fábio Luís @scanpt, Richard Zana, Billy Jheng Bing Jhong and Pan Zhenpeng (@Peterpan0927) of STAR Labs SG Pte. Ltd.
CVE-2026-84521: Billy Jheng Bing Jhong and Pan Zhenpeng (@Peterpan0927) of STAR Labs SG Pte. Ltd.– Kernel
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: An app may be able to cause unexpected system termination or corrupt kernel memory
Description: A race condition was addressed with improved state handling.
CVE-2026-84507: Billy Jheng Bing Jhong and Pan Zhenpeng (@Peterpan0927) of STAR Labs SG Pte. Ltd.– Kernel
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: An app may be able to cause unexpected system termination or corrupt kernel memory
Description: A double free issue was addressed with improved memory management.
CVE-2026-84561: Billy Jheng Bing Jhong and Pan Zhenpeng (@Peterpan0927) of STAR Labs SG Pte. Ltd., Bhaswanth Chigurupati– Kernel
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: A local user may be able to cause unexpected system termination or read kernel memory
Description: An out-of-bounds read was addressed with improved bounds checking.
CVE-2026-65359: Billy Jheng Bing Jhong and Pan Zhenpeng (@Peterpan0927) of STAR Labs SG Pte. Ltd.– libarchive
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: Processing a maliciously crafted file may lead to unexpected app termination
Description: A heap buffer overflow was addressed with improved bounds checking.
CVE-2026-86870: Kitten Food– MobileAccessoryUpdater
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: Connecting a malicious accessory may cause unexpected system termination
Description: A memory corruption issue was addressed with improved input validation.
CVE-2026-86924: Matthew Zamat– MobileBackup
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: An app may be able to modify protected parts of the file system
Description: A path handling issue was addressed with improved validation.
CVE-2026-65411: Rodolphe Brunetti (@eisw0lf) of Lupus Nova– MobileBackup
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: An attacker with physical access to a trust-paired device may be able to read and write arbitrary files
Description: A path traversal issue was addressed with improved path validation.
CVE-2026-84598: Drin Raci of sentry.security– Model I/O
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: Opening a maliciously crafted file may lead to unexpected process termination
Description: A buffer overflow was addressed with improved size validation.
CVE-2026-84497: Yiğit Can YILMAZ (@yilmazcanyigit)– Music
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: An app may be able to access sensitive user data
Description: An authorization issue was addressed with improved state management.
CVE-2026-84615: Stanislav Jelezoglo– NetworkExtension
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: An app may be able to identify what other apps a user has installed
Description: An information disclosure issue was addressed with improved state management.
CVE-2026-84626: Sindre Sorhus, Hoffcona of IES Red Team– Photos
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: An app may be able to access sensitive user data
Description: A permissions issue was addressed with additional restrictions.
CVE-2026-84491: an anonymous researcher– Power Management
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: An app may be able to fingerprint the device
Description: An authorization issue was addressed with improved state management.
CVE-2026-84623: Ilya Andr (andrd3v)– RealityKit
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: Opening a maliciously crafted file may cause unexpected process termination or disclose process memory
Description: An out-of-bounds read issue was addressed with improved input validation.
CVE-2026-84532: Hongsik Kim (mnur), stratan (@5tratan)– RealityKit
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: Processing a maliciously crafted file may lead to unexpected app termination
Description: An out-of-bounds write issue was addressed with improved bounds checking.
CVE-2026-28966: stratan (@5tratan)– Reminders
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: An app may be able to access sensitive user data
Description: This issue was addressed with improved checks.
CVE-2026-65403: Rahul Raj– Safe Browsing
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: An app may be able to access sensitive user data
Description: This issue was addressed with additional entitlement checks.
CVE-2026-86897: Stuart Wallace– SceneKit
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: Processing a maliciously crafted file may result in disclosure of process memory
Description: An integer overflow was addressed with improved input validation.
CVE-2026-84487: stratan (@5tratan), Peter Malone, Dhiyanesh Selvaraj (@redroot97)– SceneKit
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: Processing a maliciously crafted 3D model may lead to memory corruption
Description: An out-of-bounds write issue was addressed with improved bounds checking.
CVE-2026-84546: Narendra Singh (@_3P1C), stratan (@5tratan), Peter Malone
CVE-2026-84611: Nathaniel Oh (@calysteon)– SceneKit
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: Processing a maliciously crafted 3D model may lead to memory corruption
Description: The issue was addressed with improved memory handling.
CVE-2026-84632: Peter Malone– SceneKit
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: Processing a maliciously crafted 3D model may lead to memory corruption
Description: An integer overflow was addressed with improved input validation.
CVE-2026-84620: Peter Malone– SceneKit
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: Processing a maliciously crafted 3D scene may lead to unexpected process termination
Description: An out-of-bounds write issue was addressed with improved bounds checking.
CVE-2026-84526: stratan (@5tratan)– Security
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: An attacker with a compromised intermediate certificate authority may be able to issue certificates with arbitrary extended key usages
Description: A certificate validation issue was addressed with improved certificate validation.
CVE-2026-86881: Surya Narayan Kushwaha, Roman Zabicki, John Lussier, Filip Olszak– Siri Suggestions
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: An attacker with physical access to a locked device may be able to view sensitive user information
Description: A logic issue was addressed with improved checks.
CVE-2026-86890: Abhay Kailasia (@abhay_kailasia) from Safran Mumbai India– Spotlight
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: An app may be able to access sensitive user data
Description: An authorization issue was addressed with improved access control.
CVE-2026-84621: Abodi Dawoud, Ujjwal Reddy Kalvolu Sreenivasa Reddy, Johan Wahyudi, Armend Gashi– SpringBoard
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: An app may be able to cause a denial-of-service
Description: This issue was addressed with additional entitlement checks.
CVE-2026-86892: Lehan Dilusha Jayasingha– Storage
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: An app may be able to access user-sensitive data
Description: A permissions issue was addressed with additional restrictions.
CVE-2026-65345: 이재영, Seung Je Seong, Jakob Pammer, Ilya Andr (andrd3v) of Positive Technologies– Storage
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: An app may be able to modify protected parts of the file system
Description: A permissions issue was addressed with additional restrictions.
CVE-2026-65348: Jérôme Djouder– Symptom Framework
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: A malicious application may be able to determine a user’s current location
Description: A privacy issue was addressed with improved private data redaction for log entries.
CVE-2026-84513: Sindre Sorhus– TCC
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: An app may be able to modify protected system files
Description: A path traversal issue was addressed with improved input validation.
CVE-2026-86886: Constantin Clerc, Shad J, Huy Nguyen (@34306) of Calif.io, huami1314 (@huamidev), an anonymous researcher– Time Zone
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: An app may be able to bypass certain Privacy preferences
Description: A privacy issue was addressed by removing sensitive data.
CVE-2026-86887: an anonymous researcher– Watch App
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: An app may be able to track users across apps and websites without permission
Description: A privacy issue was addressed with improved state management.
CVE-2026-86904: Stanislav Jelezoglo– WebKit
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: Processing maliciously crafted web content may lead to memory corruption
Description: A use-after-free issue was addressed with improved memory management.
WebKit Bugzilla: 313577
CVE-2026-43715: Milad Nasr and Nicholas Carlini with Claude, Anthropic– WebKit Canvas
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: Processing maliciously crafted web content may lead to an unexpected Safari crash
Description: A use-after-free issue was addressed with improved memory management.
WebKit Bugzilla: 313935
CVE-2026-64718: Niels Hofmans, OGINOME Tomohito, an anonymous researcher– XPC
Available for: iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
Impact: An app may be able to access sensitive user data
Description: An authorization issue was addressed with improved state management.
CVE-2026-84617: Stuart Wallace

■関連リンク
・エスマックス(S-MAX)
・エスマックス(S-MAX) smaxjp on Twitter
・S-MAX – Facebookページ
・iOS 26 関連記事一覧 – S-MAX
・iPadOS 26 関連記事一覧 – S-MAX
・iOS 26 のアップデートについて – Apple サポート (日本)
・iPadOS 26 のアップデートについて – Apple サポート (日本)
・iOS 26.7およびiPadOS 26.7のセキュリティコンテンツについて – Apple サポート (日本)
・Apple セキュリティアップデート – Apple サポート
コメント