AppleがiOS 27やiPadOS 27、watchOS 27、tvOS 27、visionOS 27、macOS Golden Gate 27などの正式版をリリース!
Appleは14日(現地時間)、スマートフォン(スマホ)「iPhone」シリーズ向けプラットフォーム「iOS」およびタブレット「iPad」シリーズ向けプラットフォーム「iPadOS」、スマートウォッチ「Apple Watch」シリーズ向けプラットフォーム「watchOS」、スマートテレビ「Apple TV」向けプラットフォーム「tvOS」、スマートヘッドセット「Apple Vision Pro」向けプラットフォーム「visionOS」、パソコン「Mac」向けプラットフォーム「macOS」のそれぞれの最新バージョンの正式版を配信開始したとお知らせしています。
最新バージョンはiOSが「iOS 27.0(24A437)」、iPadOSが「iPadOS 27.0(24A437)」、watchOSが「watchOS 27.0(24R364)」、tvOSが「tvOS 27.0(24J361)」、visionOSが「visionOS 27.0(24M362)」、macOSが「macOS Golden Gate 27.0(26A428)」となっており、それぞれ対象製品であれば、無料でアップデートでき、iOSやiPadOSなどでは各機種ともに本体のみでネットワーク経由によるOTA(On-The-Air)でダウンロードして行えるほか、従来通りにWindowsおよびMacのパソコン(PC)を用いて各製品をUSBケーブルで接続しても行えます。
なお、iPhoneやiPadにて本体のみでのアップデートの方法は「設定」→「一般」→「ソフトウェア・アップデート」を表示し、下部にある「その他の利用可能なアップデート」のところに「iOS 27にアップグレード」や「iPadOS 27にアップグレード」をタップして実施します。対象機種はiOS 27ではiOS 26と同様にiPhone 11シリーズ以降やiPhone SE(第2世代)以降が対象で、iPadOS 27ではiPadOS 26とは異なり、iPad(第8世代)やiPad mini(第5世代)、iPad Air(第3世代)、11インチiPad Pro(第1世代)、12.9インチiPad Pro(第3世代)が対象外となり、対象外の機種ではそれぞれiPadOS 27にはアップデートできないのでご注意ください。
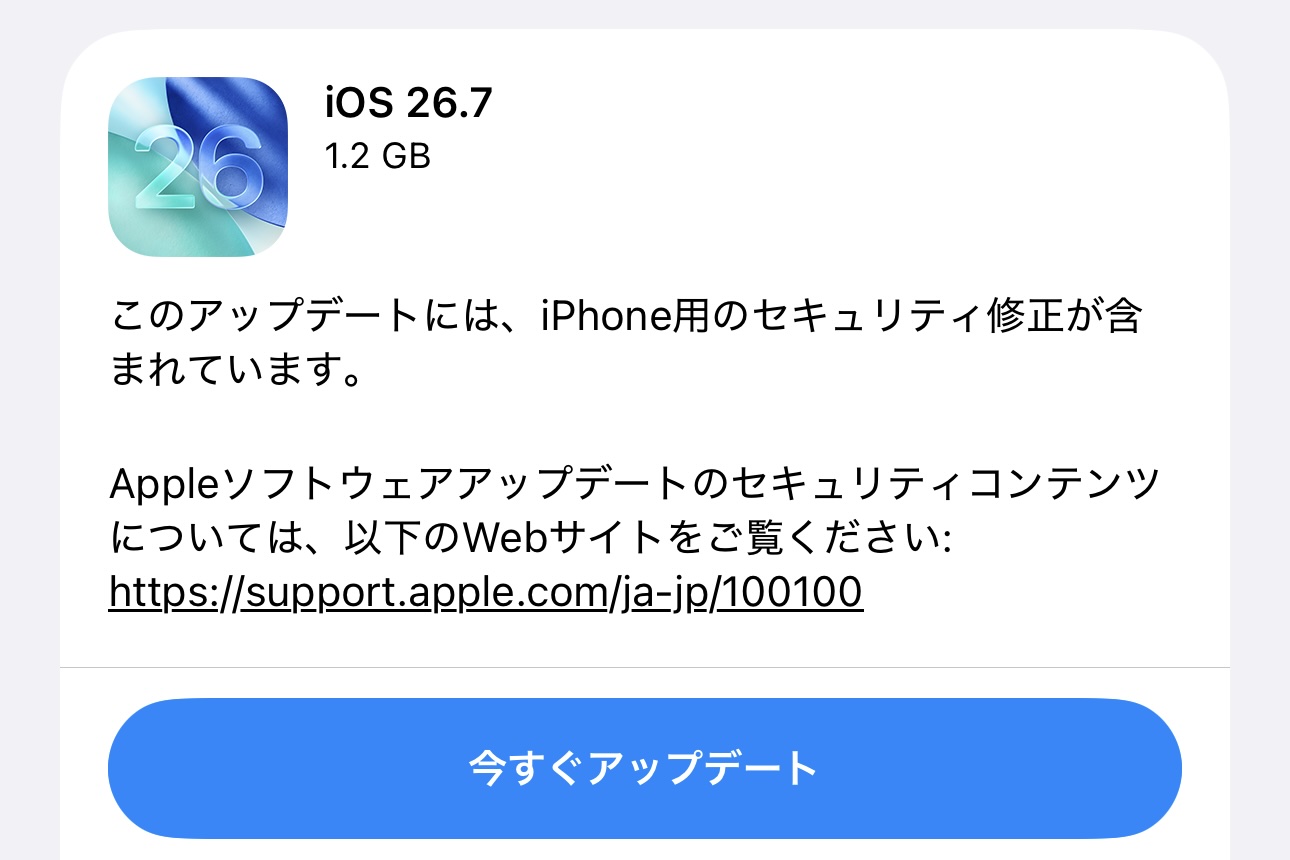
一方、すぐにiOS 27にしたくない人向けに「iOS 26」および「iPadOS 26」のアップデートもしばらく提供される見込みで、すでに紹介しているようにiOS 26およびiPadOS 26の重要な脆弱性を修正した最新バージョン「iOS 26.7」および「iPadOS 26.7」もリリースされています。その他、macOSも前バージョンの最新バージョン「macOS Tahoe 26.7」や「macOS Sequoia 15.8」なども提供開始されています。
iOS 27およびiPadOS 27は音声アシスタント「Siri」が次世代のApple Foundation Modelsを搭載して再構築された「Siri AI」として大幅アップグレードされ、Siriとの会話履歴をプライベートに同期して過去の会話を振り返ったり、会話の続きをMacやApple Watchで行ったりすることが可能になるほか、画面認識や文脈理解などにも対応し、さらにカメラを使った「Visual Intelligence」機能が追加されます。また「Apple Intelligence」もGoogleのAI機能「Gemini」と統合されてさまざまなアプリと連携できるようになるとのこと。
加えて子供向けの「ペアレンタルコントロール」もかなり強化され、新しい「Child Account」(子供用アカウント)やスクリーンタイムの刷新で「ゲーム」や「SNS」などを個別に時間制限できる「Time Allowances」(時間制限)などが追加され、他にも動作が高速化されたり、デザイン面では「Liquid Glass」が進化して設されたスライダーを使って「透明」から「色付」まで好みに応じて透明度や色合いを調整できるようになったり、ヘルスケア機能では周期記録において閉経周辺期や更年期のサポートが追加されるなどするということです。詳細は以下の記事や公式Webサイトをご確認ください。
・Apple、スマホ向け次期プラットフォーム「iOS 27」を発表!iPhone 11以降が対象で正式版が今秋登場。Siri AIやChild Accountなどが追加 – S-MAX
・Apple、タブレット向け次期プラットフォーム「iPadOS 27」を発表!iPad(第8世代)やmini(第5世代)、Air(第3世代)などは対象外に – S-MAX
アップデートはiOS 15やiPadOS 15から一時的に既存のOSバージョンのままにする機能が導入されているため、iOS 27やiPadOS 27にするためには「ソフトウェア・アップデート」の画面の下部に「その他の利用可能なアップデート」として「iOS 27にアップグレード」や「iPadOS 27にアップグレード」が表示されるのでそこからアップデートを行います。なお、しばらくは最新メジャーバージョンにアップグレードせずにiOS 26およびiPadOS 26のままでセキュリティーアップデートを適用できるようになっています。
<「iOS 27」対応機種>
・iPhone Duo
・iPhone 18 Pro Max
・iPhone 18 Pro
・iPhone 17 Pro Max
・iPhone 17 Pro
・iPhone Air
・iPhone 17
・iPhone 17e
・iPhone 16 Pro Max
・iPhone 16 Pro
・iPhone 16 Plus
・iPhone 16
・iPhone 16e
・iPhone 15 Pro Max
・iPhone 15 Pro
・iPhone 15 Plus
・iPhone 15
・iPhone 14 Pro Max
・iPhone 14 Pro
・iPhone 14 Plus
・iPhone 14
・iPhone 13 Pro Max
・iPhone 13 Pro
・iPhone 13
・iPhone 13 mini
・iPhone 12 Pro Max
・iPhone 12 Pro
・iPhone 12
・iPhone 12 mini
・iPhone 11 Pro Max
・iPhone 11 Pro
・iPhone 11
・iPhone SE(第2世代)
・iPhone SE(第3世代)
<「iPadOS 27」対応機種>
・iPad(第9世代)
・iPad(第10世代)
・iPad(A16)
・iPad mini(第6世代)
・iPad mini(A17 Pro)
・iPad Air(第4世代)
・iPad Air(第5世代)
・11インチiPad Air(M2)
・11インチiPad Air(M3)
・11インチiPad Air(M4)
・13インチiPad Air(M2)
・13インチiPad Air(M3)
・13インチiPad Air(M4)
・11インチiPad Pro(第2世代)
・11インチiPad Pro(第3世代)
・11インチiPad Pro(第4世代)
・11インチiPad Pro(M4)
・11インチiPad Pro(M5)
・12.9インチiPad Pro(第4世代)
・12.9インチiPad Pro(第5世代)
・12.9インチiPad Pro(第6世代)
・13インチiPad Pro(M4)
・13インチiPad Pro(M5)
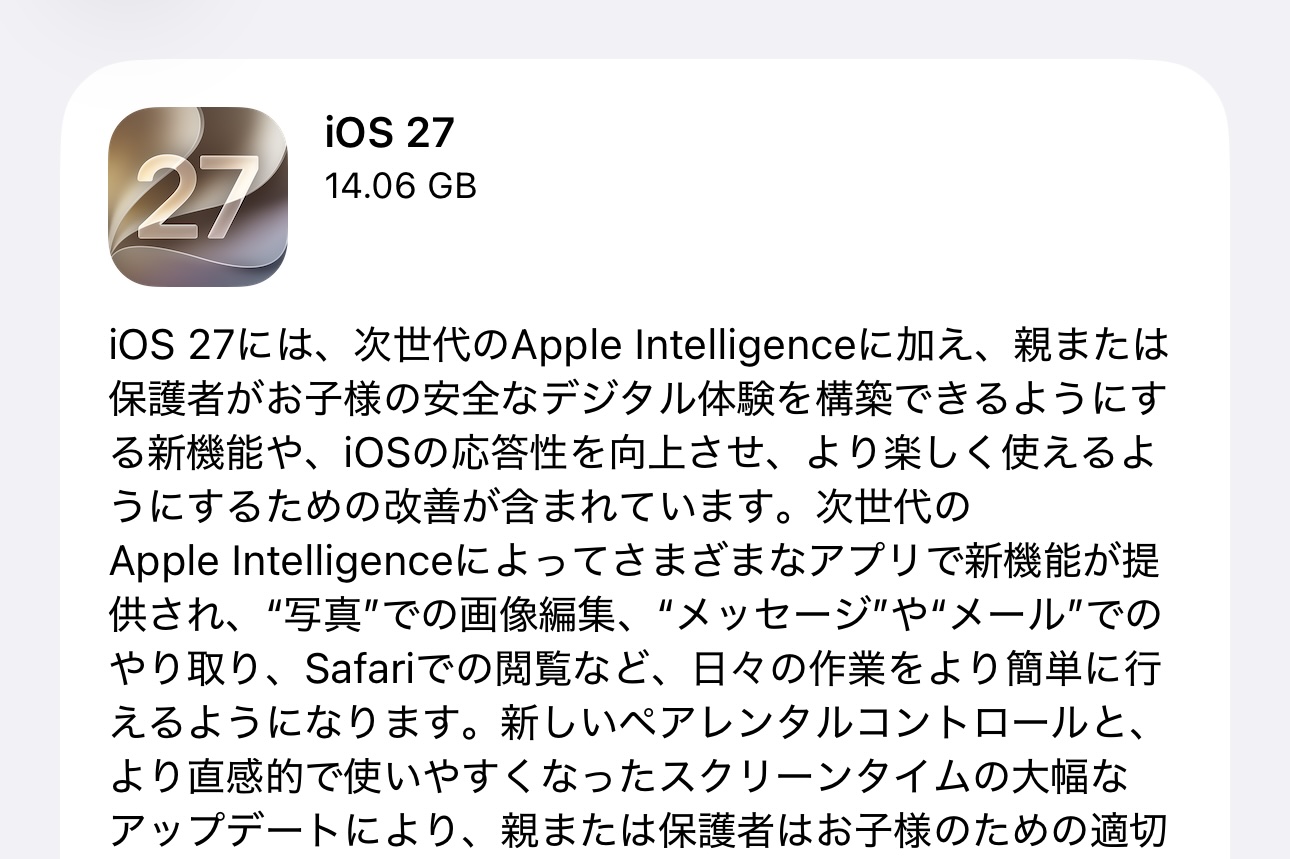
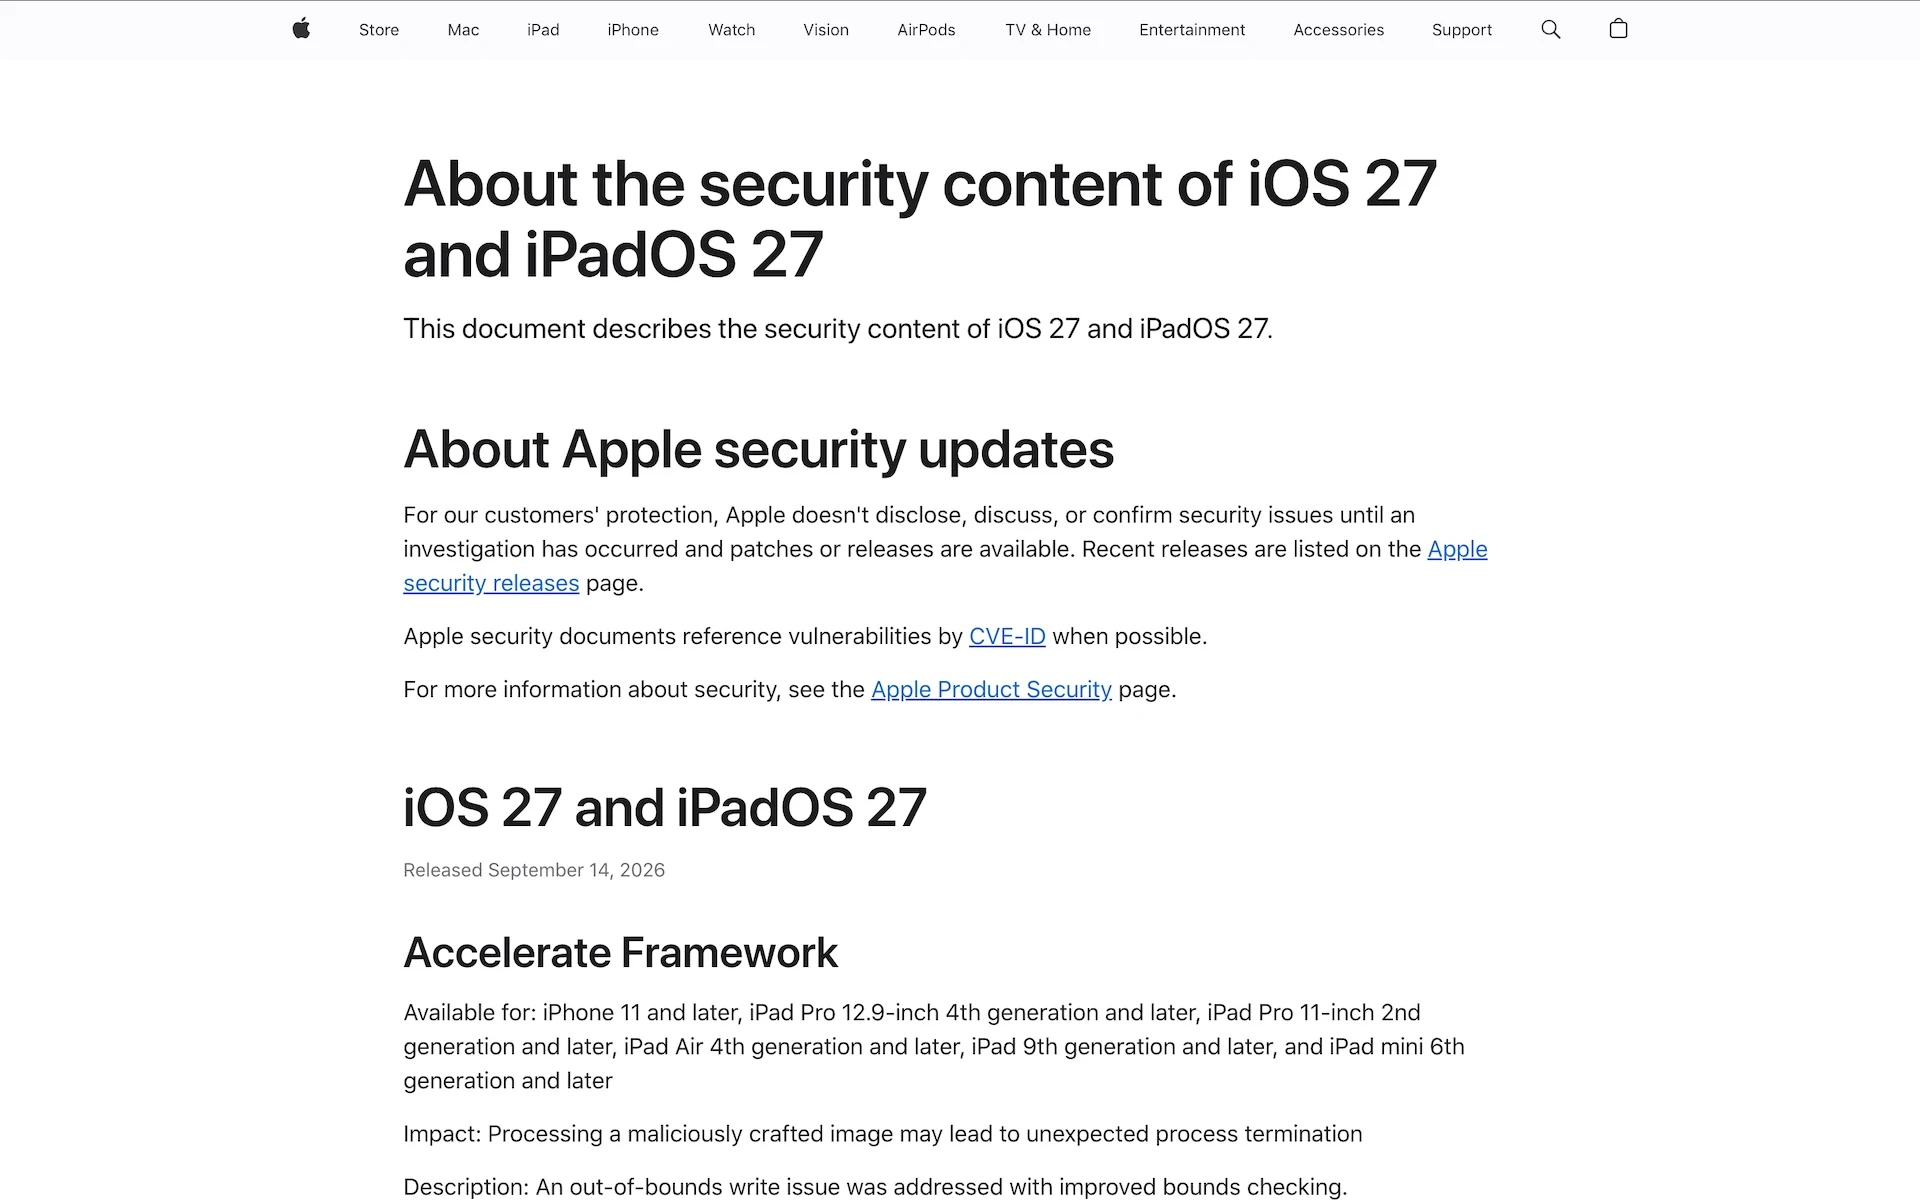
単体でアップデートする場合のダウンロードサイズは手持ちのiPhone 15 Pro MaxでiOS 27.6.2からだと14.06GBとなっています。なお、Appleが案内しているアップデートの内容およびセキュリティーコンテンツの修正は以下の通り。なお、Appleではアップデートに向けてバックアップをしっかりと取っておくことをオススメしているほか、いくつかのアプリでは動作確認が取れるまでアップデートを待つように案内しています。その他、手元のiPhone 15 Pro Maxなどでは各仮想移動体通信事業者(MVNO)でも「mineo」のAプラン(VoLTE対応)などのau回線を用いたサービスも含めて引き続き利用できていますが、どうしても心配な人は公式の動作確認を待ってみてください。
iOS 27 and iPadOS 27
Released September 14, 2026– Accelerate Framework
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: Processing a maliciously crafted image may lead to unexpected process termination
Description: An out-of-bounds write issue was addressed with improved bounds checking.
CVE-2026-86882: Peter Malone– Accessibility
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to access sensitive user data
Description: This issue was addressed with improved data protection.
CVE-2026-43664: Stuart Wallace, Ilya Andr (andrd3v), Rosyna Keller of Totally Not Malicious Software, CJ Vana, David Strnadel, Daniel Febrero, Asaf Cohen, Gongyu Ma (@Mezone0), Jian Lee (@speedyfriend433)– Accessibility
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to identify what other apps a user has installed
Description: A privacy issue was addressed with improved handling of user preferences.
CVE-2026-64761: Stuart Wallace, Sindre Sorhus– Accounts
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: A malicious application may be able to bypass Privacy preferences
Description: An authorization issue was addressed with improved state management.
CVE-2026-65404: Arni Hardarson (Neonix Security), Vinay Kumar Rasala (Xplo8E) from Appknox, Stuart Wallace, 이재영– APFS
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to cause unexpected system termination or write kernel memory
Description: An out-of-bounds write issue was addressed with improved bounds checking.
CVE-2026-84523: Cem Onat Karagun, an anonymous researcher– App Store
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: A local app may be able to read a persistent account identifier
Description: A permissions issue was addressed with additional restrictions.
CVE-2026-86888: Zhongcheng Li (CK01)– Apple Account
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to use the Sign In With Apple authentication flow to access the user’s Apple Account
Description: An authentication issue was addressed with improved state management.
CVE-2026-20683: Dem0ns (@天府简易信工作室), Abdelhak Kherroubi, Jasminder Pal Singh, Lehan Dilusha Jayasingha (Sri Lanka)– Apple Neural Engine
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to cause unexpected system termination
Description: An integer overflow was addressed with improved input validation.
CVE-2026-65408: tamdao– AppleAVD
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to cause unexpected system termination
Description: A use after free issue was addressed with improved memory management.
CVE-2026-65407: Franco Belman at Blackwing Intelligence– AppleDouble
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: Mounting a disk image with maliciously crafted files may lead to unexpected system termination
Description: An out-of-bounds write issue was addressed with improved bounds checking.
CVE-2026-84519: Richard Zana– AppleKeyStore
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to cause unexpected system termination
Description: A use after free issue was addressed with improved memory management.
CVE-2026-84593: Meta Red Team X – Nik Tsytsarkin, Alexandre Borges– Authentication Services
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to delete credentials stored in Keychain
Description: This issue was addressed by removing the vulnerable code.
CVE-2026-86905: Ilya Andr (andrd3v)– AuthKit
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: A local app may be able to read a persistent account identifier
Description: A permissions issue was addressed with additional restrictions.
CVE-2026-84583: Zhongcheng Li from IES Red Team– AVEVideoEncoder
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to cause unexpected system termination
Description: The issue was addressed with improved checks.
CVE-2026-65410: Calif.io in collaboration with Claude and Anthropic Research– AVEVideoEncoder
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to cause unexpected system termination
Description: A type confusion issue was addressed with improved memory handling.
CVE-2026-84616: Peter Malone– AVEVideoEncoder
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: A sandboxed app may be able to execute arbitrary code with kernel privileges
Description: A race condition was addressed with improved state management.
CVE-2026-84607: Ruslan Dautov– BackgroundAssets
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to access sensitive user data
Description: A logic issue was addressed with improved validation.
CVE-2026-65406: Ye Zhang (@VAR10CK) of Baidu Security– Baseband
Available for: iPhone 11 and later
Impact: An attacker in radio range may be able to cause unexpected system termination
Description: An input validation issue was addressed with improved input validation.
CVE-2026-86885: Tuan D. Hoang, Hazem Issa, and Yongdae Kim @ KAIST SysSec Lab– Baseband
Available for: iPhone 11 and later
Impact: A remote attacker may be able to cause a denial-of-service
Description: A denial-of-service issue was addressed with improved input validation.
CVE-2026-86879: Hazem Issa and Yongdae Kim @ SysSec, KAIST– Bluetooth
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: A remote attacker may be able to cause unexpected app termination or arbitrary code execution
Description: An out-of-bounds write issue was addressed with improved bounds checking.
CVE-2026-65414– Bluetooth
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may gain unauthorized access to Bluetooth
Description: An authorization issue was addressed with improved state management.
CVE-2026-84560: an anonymous researcher– Camera
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to access sensitive user data
Description: A permissions issue was addressed with additional restrictions.
CVE-2026-86878: Sindre Sorhus, Ilya Andr (andrd3v) of Positive Technologies, Asaf Cohen– CloudKit
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: A local app may be able to read a persistent account identifier
Description: An information disclosure issue was addressed with improved state management.
CVE-2026-86895: Stanislav Jelezoglo– CloudKit
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to read device name
Description: A permissions issue was addressed with additional restrictions.
CVE-2026-86893: Heiner Gerdes– copyfile
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An archive may be able to bypass Gatekeeper
Description: A file quarantine bypass was addressed with additional checks.
CVE-2026-65399: Rishabh Jain (rjcyber) of cyberplanet, Pasquale Scola, an anonymous researcher– CoreMedia
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: Processing a maliciously crafted image may lead to arbitrary code execution
Description: A memory corruption issue was addressed by removing the vulnerable code.
CVE-2026-64752: Nik Tsytsarkin– CoreMedia
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: A sandboxed process may be able to circumvent sandbox restrictions
Description: An out-of-bounds write issue was addressed with improved bounds checking.
CVE-2026-86876: Chris Bailey – Short Circuit– CoreMedia
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: Processing a maliciously crafted video file may lead to unexpected app termination
Description: An out-of-bounds write issue was addressed with improved bounds checking.
CVE-2026-65344: Siyeong kim– CoreML
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: A sandboxed app may be able to access restricted files
Description: A permissions issue was addressed with improved path validation.
CVE-2026-84624: AL Najafi, tamdao– CoreMotion
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to access motion data from headphones without user consent
Description: An authorization issue was addressed with improved validation.
CVE-2026-43737: Stuart Wallace– CoreText
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: Processing web content may lead to a denial-of-service
Description: A null pointer dereference was addressed with improved input validation.
CVE-2026-65412: Pavan Nallamothu– CoreText
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: Processing a maliciously crafted font may result in the disclosure of process memory
Description: An out-of-bounds read was addressed with improved bounds checking.
CVE-2026-84596: ret2happy, Meta Product Security– CoreUI
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: Processing a maliciously crafted file may lead to unexpected app termination
Description: An out-of-bounds write issue was addressed with improved bounds checking.
CVE-2026-84575: Mustafa Calap (@ordinal0, dbg.re)– CoreUI
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to cause a denial of service
Description: A buffer overflow was addressed with improved bounds checking.
CVE-2026-84489: stratan (@5tratan), Peter Malone– CoreUI
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: Processing a maliciously crafted image may lead to unexpected app termination
Description: A buffer overflow was addressed with improved bounds checking.
CVE-2026-84571: stratan (@5tratan), Peter Malone– CoreUI
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: Processing a maliciously crafted asset catalog may result in disclosure of process memory
Description: The issue was addressed with improved memory handling.
CVE-2026-43738: Peter Malone– CoreUI
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: Processing a maliciously crafted asset catalog may lead to unexpected process termination
Description: An out-of-bounds write issue was addressed with improved bounds checking.
CVE-2026-84511: Rahul Raj, stratan (@5tratan)– DeviceCheck
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to read persistent device identifiers
Description: An authorization issue was addressed with improved access control.
CVE-2026-84612: N.M.Praveen Nawarathne (@zblockrat), James Gill (@jjtech@infosec.exchange)– Disk Images
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to cause unexpected system termination
Description: The issue was addressed with improved memory handling.
CVE-2026-84552: Tommy DeVoss from Braze Security Team (@thedawgyg), flower xu, Adriatik Raci, PETOWORKS의 Bugeun Choi (@Bugeun), Peter Malone, Daisuke Hatakeyama and Ryohei Ueki (@SYZD Research), Hyunwoo Kim (@v4bel)– exFAT
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: Mounting a maliciously crafted volume may lead to unexpected system termination
Description: A heap buffer overflow was addressed with improved bounds checking.
CVE-2026-84510: Meta Red Team X – Nik Tsytsarkin, Richard Zana– File Bookmark
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to modify a file it only had permission to read
Description: A permissions issue was addressed with additional restrictions.
CVE-2026-43785: Junyeong Lee (jylab.github.io), Merrick Hare, Aditya Kumar, John Nzyuko Uvyu, Narendra Singh (@_3P1C)– file_cmds
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: Extracting a maliciously crafted archive may allow an attacker to write arbitrary files
Description: A path handling issue was addressed with improved validation.
CVE-2026-84534: Geoffrey Lovelace– Filters
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: Processing a maliciously crafted file may lead to unexpected app termination
Description: A memory corruption issue was addressed with improved input validation.
CVE-2026-43688: Peter Malone– FontParser
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: Processing a maliciously crafted font file may lead to unexpected app termination
Description: An out-of-bounds read was addressed with improved bounds checking.
CVE-2026-84524: an anonymous researcher– FontParser
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: Processing a maliciously crafted font may result in the disclosure of process memory
Description: An out-of-bounds read issue was addressed with improved input validation.
CVE-2026-84597: Nik Tsytsarkin– Foundation
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to cause a denial of service
Description: A type confusion issue was addressed with improved memory handling.
CVE-2026-65409: Bruce Dang of Calif.io in collaboration with Claude and Anthropic Research– Graphics
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to cause unexpected system termination
Description: A race condition was addressed with improved state handling.
CVE-2026-84492: Tommy DeVoss from Braze Security Team (@thedawgyg), Jiyong Yang– Heimdal
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An attacker in a privileged network position may be able to modify network traffic
Description: A cryptographic issue was addressed with improved integrity checks.
CVE-2026-84533: Vishal Patidar, Roman Zabicki– iCloud
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to identify a user across reinstalls
Description: A privacy issue was addressed with improved handling of identifiers.
CVE-2026-84606: Ilya Andr (andrd3v)– Image Capture
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to access user-sensitive data
Description: A path handling issue was addressed with improved validation.
CVE-2026-64756: Luke Symons– ImageIO
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: Processing a maliciously crafted image may result in disclosure of process memory
Description: An uninitialized memory issue was addressed with improved memory initialization.
CVE-2026-84564: Justin O’Leary– ImageIO
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: Processing a maliciously crafted image may result in memory corruption
Description: An out-of-bounds write issue was addressed with improved bounds checking.
CVE-2026-65395: Mateusz Jurczyk of Google Project Zero, Varik Matevosyan– IOKit
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to cause unexpected system termination
Description: A use after free issue was addressed with improved memory management.
CVE-2026-28969: Mihalis Haatainen, Ashish Kunwar, Ari Hawking, 이재영– IOMobileFrameBuffer
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to cause unexpected system termination or corrupt kernel memory
Description: An out-of-bounds access issue was addressed with improved bounds checking.
CVE-2026-65398: Chris Bailey – Short Circuit, Mustafa Calap (@ordinal0, dbg.re), David Strnadel, Meta Red Team X – Nik Tsytsarkin– IOSurfaceAccelerator
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to leak sensitive kernel state
Description: An information leakage was addressed with additional validation.
CVE-2026-64760: an anonymous researcher, Seiji Sakurai (@HeapSmasher), Franco Belman at Blackwing Intelligence– iWork
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: A malicious app may be able to break out of its sandbox
Description: A permissions issue was addressed with additional restrictions.
CVE-2026-65354: Csaba Fitzl (@theevilbit) of Iru– Kernel
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to cause unexpected system termination or corrupt kernel memory
Description: An out-of-bounds write issue was addressed with improved bounds checking.
CVE-2026-28968: genter0, Svetoslav Stolarov & Aisa Fox, Josh Maine of Calif.io, Dun– Kernel
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: A local attacker may be able to cause unexpected system termination or corrupt kernel memory
Description: The issue was addressed with improved memory handling.
CVE-2026-84566: Bernhard Jackiewicz– Kernel
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: A local user may be able to cause unexpected system termination or read kernel memory
Description: A race condition was addressed with additional validation.
CVE-2026-65415: Billy Jheng Bing Jhong and Pan Zhenpeng (@Peterpan0927) of STAR Labs SG Pte. Ltd., Ryan Hileman via Xint Code (xint.io)– Kernel
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to cause unexpected system termination or corrupt kernel memory
Description: A double free issue was addressed with improved memory management.
CVE-2026-84561: Billy Jheng Bing Jhong and Pan Zhenpeng (@Peterpan0927) of STAR Labs SG Pte. Ltd., Bhaswanth Chigurupati– Kernel
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to cause unexpected system termination
Description: A race condition was addressed with improved state handling.
CVE-2026-84630: Tristan Madani (@TristanInSec) from Talence Security
CVE-2026-65360: Billy Jheng Bing Jhong and Pan Zhenpeng (@Peterpan0927) of STAR Labs SG Pte. Ltd.
CVE-2026-65358: Billy Jheng Bing Jhong and Pan Zhenpeng (@Peterpan0927) of STAR Labs SG Pte. Ltd.– Kernel
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to cause unexpected system termination
Description: A memory corruption issue was addressed with improved memory handling.
CVE-2026-65377: Billy Jheng Bing Jhong and Pan Zhenpeng (@Peterpan0927) of STAR Labs SG Pte. Ltd., Ye Zhang (@VAR10CK) of Baidu Security– Kernel
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app with root privileges may be able to read uninitialized kernel memory
Description: A memory initialization issue was addressed with improved memory handling.
CVE-2026-84622: Hiroki Imai (LAC Co., Ltd.)– Kernel
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: A malicious app may be able to gain root privileges
Description: A permissions issue was addressed with additional restrictions.
CVE-2026-43689: Andreas Jaegersberger & Ro Achterberg of Nosebeard Labs– Kernel
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: Connecting to a malicious NFS server may disclose kernel memory
Description: The issue was addressed with improved memory handling.
CVE-2026-43687: R4mbb of KRsecurity, Peter Malone– Kernel
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: Connecting to a malicious NFS server may lead to kernel memory corruption
Description: A use-after-free issue was addressed with improved memory management.
CVE-2026-43686: Peter Malone– Kernel
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to determine kernel memory layout
Description: A memory initialization issue was addressed with improved memory handling.
CVE-2026-65405: Billy Jheng Bing Jhong and Pan Zhenpeng (@Peterpan0927) of STAR Labs SG Pte. Ltd.– Kernel
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to disclose kernel memory
Description: An information disclosure issue was addressed with improved memory management.
CVE-2026-84530: Vladislav Shevchenko (Positive Technologies)– Kernel
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to cause unexpected system termination
Description: A use after free issue was addressed with improved memory management.
CVE-2026-84521: Billy Jheng Bing Jhong and Pan Zhenpeng (@Peterpan0927) of STAR Labs SG Pte. Ltd.
CVE-2026-65402: Fábio Luís @scanpt, Richard Zana, Billy Jheng Bing Jhong and Pan Zhenpeng (@Peterpan0927) of STAR Labs SG Pte. Ltd.– Kernel
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: A local user may be able to cause unexpected system termination or read kernel memory
Description: An out-of-bounds read was addressed with improved bounds checking.
CVE-2026-65359: Billy Jheng Bing Jhong and Pan Zhenpeng (@Peterpan0927) of STAR Labs SG Pte. Ltd.– Kernel
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to cause unexpected system termination or corrupt kernel memory
Description: A race condition was addressed with improved state handling.
CVE-2026-84507: Billy Jheng Bing Jhong and Pan Zhenpeng (@Peterpan0927) of STAR Labs SG Pte. Ltd.– Kernel
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to disclose kernel memory
Description: An out-of-bounds read was addressed with improved input validation.
CVE-2026-86903: Billy Jheng Bing Jhong and Pan Zhenpeng (@Peterpan0927) of STAR Labs SG Pte. Ltd.– Kernel
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to cause unexpected system termination
Description: A type confusion issue was addressed with improved checks.
CVE-2026-84602: Billy Jheng Bing Jhong and Pan Zhenpeng (@Peterpan0927) of STAR Labs SG Pte. Ltd.– libarchive
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: Processing a maliciously crafted file may lead to unexpected app termination
Description: A heap buffer overflow was addressed with improved bounds checking.
CVE-2026-86870: Kitten Food– Managed Configuration
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to access sensitive user data
Description: A privacy issue was addressed with improved handling of files.
CVE-2026-86883: Sindre Sorhus, Morris Richman (@morrisinlife), Stuart Wallace, Tristan Brennan– MediaRemote
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: A sandboxed app may be able to access the System Keychain
Description: An authorization issue was addressed with improved state management.
CVE-2026-84628: Myeonghun Pak, Nathaniel Oh (@calysteon), Alan Banderas (@creeper4004)– MobileAccessoryUpdater
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: Connecting a malicious accessory may cause unexpected system termination
Description: A memory corruption issue was addressed with improved input validation.
CVE-2026-86924: Matthew Zamat– MobileBackup
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to modify protected parts of the file system
Description: A path handling issue was addressed with improved validation.
CVE-2026-65411: Rodolphe Brunetti (@eisw0lf) of Lupus Nova– MobileBackup
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An attacker with physical access to a trust-paired device may be able to read and write arbitrary files
Description: A path traversal issue was addressed with improved path validation.
CVE-2026-84598: Drin Raci of sentry.security– Model I/O
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: Opening a maliciously crafted file may lead to unexpected process termination
Description: A buffer overflow was addressed with improved size validation.
CVE-2026-84497: Yiğit Can YILMAZ (@yilmazcanyigit)– Music
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to access sensitive user data
Description: An authorization issue was addressed with improved state management.
CVE-2026-84615: Stanislav Jelezoglo– NetworkExtension
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to access sensitive user data
Description: An authorization issue was addressed with improved state management.
CVE-2026-43695: Claudio Bozzato and Francesco Benvenuto of Cisco Talos– NetworkExtension
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to identify what other apps a user has installed
Description: An information disclosure issue was addressed with improved state management.
CVE-2026-84626: Sindre Sorhus, Hoffcona of IES Red Team– Photos Storage
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to access sensitive user data
Description: A permissions issue was addressed with additional restrictions.
CVE-2026-84491: an anonymous researcher– Photos Storage
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to fingerprint the user
Description: This issue was addressed with additional entitlement checks.
CVE-2026-84629: Stanislav Jelezoglo– Power Management
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to fingerprint the device
Description: An authorization issue was addressed with improved state management.
CVE-2026-84623: Ilya Andr (andrd3v)– RealityKit
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: Processing a maliciously crafted file may lead to unexpected app termination
Description: An out-of-bounds write issue was addressed with improved bounds checking.
CVE-2026-28966: stratan (@5tratan)– RealityKit
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: Opening a maliciously crafted file may cause unexpected process termination or disclose process memory
Description: An out-of-bounds read issue was addressed with improved input validation.
CVE-2026-84532: Hongsik Kim (mnur), stratan (@5tratan)– Reminders
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to access sensitive user data
Description: This issue was addressed with improved checks.
CVE-2026-65403: Rahul Raj– Safari
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: A malicious website may be able to determine what apps a user has installed
Description: This issue was addressed through improved state management.
CVE-2026-84518: Bálint Magyar (balintmagyar.com)– Safe Browsing
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to access sensitive user data
Description: This issue was addressed with additional entitlement checks.
CVE-2026-86897: Stuart Wallace– Sandbox
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to bypass network restrictions
Description: A logic issue was addressed with improved validation.
CVE-2026-84551: Issa Sancho– Sandbox Profiles
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to fingerprint the user
Description: A permissions issue was addressed with additional sandbox restrictions.
CVE-2026-84625: Ilya Andr (andrd3v) of Positive Technologies, CJ Vana– Sandbox Profiles
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to access sensitive user data
Description: A permissions issue was addressed with additional restrictions.
CVE-2026-84603: Gongyu Ma (@Mezone0), CJ Vana, Stanislav Jelezoglo– SceneKit
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: Processing a maliciously crafted file may result in disclosure of process memory
Description: An integer overflow was addressed with improved input validation.
CVE-2026-84487: stratan (@5tratan), Dhiyanesh Selvaraj (@redroot97), Peter Malone– SceneKit
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: Processing a maliciously crafted 3D model may lead to memory corruption
Description: The issue was addressed with improved memory handling.
CVE-2026-84632: Peter Malone– SceneKit
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: Processing a maliciously crafted 3D model may lead to memory corruption
Description: An integer overflow was addressed with improved input validation.
CVE-2026-84620: Peter Malone– SceneKit
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: Processing a maliciously crafted 3D model may lead to memory corruption
Description: An out-of-bounds write issue was addressed with improved bounds checking.
CVE-2026-84546: Narendra Singh (@_3P1C), stratan (@5tratan), Peter Malone
CVE-2026-84611: Nathaniel Oh (@calysteon)– SceneKit
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: Processing a maliciously crafted 3D scene may lead to unexpected process termination
Description: An out-of-bounds write issue was addressed with improved bounds checking.
CVE-2026-84526: stratan (@5tratan)– Security
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An attacker with a compromised intermediate certificate authority may be able to issue certificates with arbitrary extended key usages
Description: A certificate validation issue was addressed with improved certificate validation.
CVE-2026-86881: Surya Narayan Kushwaha, Roman Zabicki, John Lussier, Filip Olszak– Security
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: Processing maliciously crafted NTLM input may lead to unexpected app termination
Description: An out-of-bounds write issue was addressed with improved bounds checking.
CVE-2026-84531: Meshaal (@unrealmesh)– Shortcuts
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: A malicious shortcut may be able to send messages without user confirmation
Description: An authorization issue was addressed with improved state management.
CVE-2026-84600: Owen Pawling (@owenpawling)– Siri
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to access sensitive user data
Description: A permissions issue was addressed with additional restrictions.
CVE-2026-86884: Stanislav Jelezoglo, Gongyu Ma (twitter @Mezone0)– Siri Suggestions
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An attacker with physical access to a locked device may be able to view sensitive user information
Description: A logic issue was addressed with improved checks.
CVE-2026-86890: Abhay Kailasia (@abhay_kailasia) from Safran Mumbai India– Software Update
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to modify protected system files
Description: A permissions issue was addressed with improved path validation.
CVE-2026-84609: YingMuo (@YingMuo) of DEVCORE Research Team– Spotlight
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to access sensitive user data
Description: An authorization issue was addressed with improved access control.
CVE-2026-84621: Abodi Dawoud, Armend Gashi, Ujjwal Reddy Kalvolu Sreenivasa Reddy, Johan Wahyudi– SpringBoard
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to cause a denial-of-service
Description: This issue was addressed with additional entitlement checks.
CVE-2026-86892: Lehan Dilusha Jayasingha– Storage
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to modify protected parts of the file system
Description: A permissions issue was addressed with additional restrictions.
CVE-2026-65348: Jérôme Djouder– Storage
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to access user-sensitive data
Description: A permissions issue was addressed with additional restrictions.
CVE-2026-65345: Seung Je Seong, Ilya Andr (andrd3v) of Positive Technologies, Jakob Pammer, 이재영– Symptom Framework
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: A malicious application may be able to determine a user’s current location
Description: A privacy issue was addressed with improved private data redaction for log entries.
CVE-2026-84513: Sindre Sorhus– TCC
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to modify protected system files
Description: A path traversal issue was addressed with improved input validation.
CVE-2026-86886: Constantin Clerc, Shad J, huami1314 (@huamidev), Huy Nguyen (@34306) of Calif.io, an anonymous researcher– TCC
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to access sensitive user data
Description: A logging issue was addressed with improved data redaction.
CVE-2026-84527: Zeyang Li&Yuxiang Wang of Chongqing Telecom– Telephony
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An attacker in a privileged network position may be able to bypass IPSec authentication and intercept network traffic
Description: An authentication issue was addressed with improved state management.
CVE-2026-65329: Bedran Karakoc, Tobias Funke, Jacopo Clark, Katharina Kohls of Ruhr University Bochum– Time Zone
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to bypass certain Privacy preferences
Description: A privacy issue was addressed by removing sensitive data.
CVE-2026-86887: an anonymous researcher– Watch App
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to track users across apps and websites without permission
Description: A privacy issue was addressed with improved state management.
CVE-2026-86904: Stanislav Jelezoglo– WebKit
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: Processing maliciously crafted web content may lead to an unexpected process termination
Description: A logic issue was addressed with improved state management.
WebKit Bugzilla: 310457
CVE-2026-84635: Souta Sugiyama– WebKit
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: Processing maliciously crafted web content may disclose sensitive user information
Description: A permissions issue was addressed by removing the vulnerable code.
WebKit Bugzilla: 315121
CVE-2026-64753: Viggo Lekdorf– WebKit
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: Opening a maliciously crafted webarchive file may lead to universal cross-site scripting
Description: A logic issue was addressed with improved state management.
WebKit Bugzilla: 3182711
CVE-2026-86898: Tomi Garcia (archyxsec)– WebKit Canvas
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: Processing maliciously crafted web content may lead to an unexpected Safari crash
Description: A use-after-free issue was addressed with improved memory management.
WebKit Bugzilla: 313935
CVE-2026-64718: Niels Hofmans, OGINOME Tomohito, an anonymous researcher– Wi-Fi3
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An attacker with physical access to an unlocked device may be able to view Wi-Fi passwords without authentication
Description: An authentication issue was addressed with improved state management.
CVE-2026-43674: Yusuf Kelany– Wi-Fi Connectivity
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to access sensitive user data
Description: An authorization issue was addressed with improved state management.
CVE-2026-84636: Jian Lee (@speedyfriend433)– XPC
Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An app may be able to access sensitive user data
Description: An authorization issue was addressed with improved state management.
CVE-2026-84617: Stuart Wallace

■関連リンク
・エスマックス(S-MAX)
・エスマックス(S-MAX) smaxjp on Twitter
・S-MAX – Facebookページ
・Apple iOS 27 関連記事一覧 – S-MAX
・Apple iPadOS 27 関連記事一覧 – S-MAX
・Major updates for Apple’s software platforms are now available – Apple
・Siri AI, a profoundly more capable and personal assistant, is here – Apple
・Apple’s new child safety features now available – Apple
・iOS 26 のアップデートについて – Apple サポート (日本)
・iPadOS 26 のアップデートについて – Apple サポート (日本)
・iOS 27およびiPadOS 27のセキュリティコンテンツについて – Apple サポート (日本)
・Apple セキュリティアップデート – Apple サポート
・OS – iOS 27 – Apple(日本)
・OS – iPadOS 27 – Apple(日本)
コメント